
Cookie
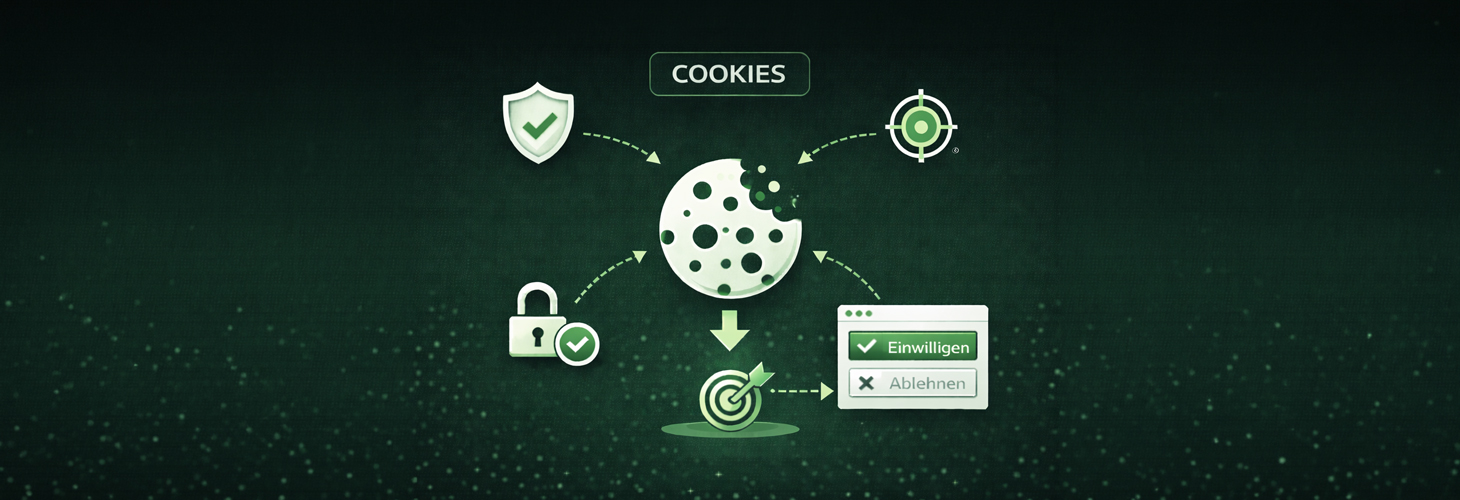
On the internet, a cookie is a small text file that a website stores in the user's browser. It contains information such as a session ID, settings or an identifier for recognition, as well as an expiry date. On later visits, the browser sends the cookie back to the website. Some cookies are deleted when the browser is closed (session cookies), others remain stored for a set period (persistent cookies).
The technology was developed in 1994 by the American programmer Lou Montulli at Netscape. He was looking for a way for websites to remember visitors – for example the contents of a shopping cart. He derived the name from the term “magic cookie”, which programmers had already used for small data packets used for identification.
First-party and third-party cookies
There are two types. First-party cookies are set by the website the user is currently visiting – for example for the shopping cart, login or the site's own web analytics. Third-party cookies, on the other hand, come from other domains, such as advertising networks. Among other things, they are used for retargeting: the visitor is tagged and later shown matching ads on other websites.
Benefits and criticism
Cookies make many websites easier to use: they keep users logged in, store settings and make sure the shopping cart is kept in an online shop. At the same time, they are used to track users' behaviour over long periods and across several websites. This is exactly where the criticism comes in: data protection advocates see it as a significant intrusion into privacy. That's why users today must be able to decide for themselves which cookies they accept – and rejecting them must be just as easy as accepting them.
Manipulative methods: unwanted!
Because the browser can be clearly recognised, websites can track users and serve them targeted advertising. Visits to different websites can also be attributed to one user in this way. Dubious providers also use cookies manipulatively, for example in cookie dropping in affiliate marketing, where commission cookies are set without a real click. This is one of the reasons why the European Union adopted the so-called Cookie Directive (2009/136/EC) in 2009 as part of the ePrivacy rules.
GDPR & co.: the current legal situation in the EU
In addition to the ePrivacy Directive, the General Data Protection Regulation (GDPR) has governed the handling of personal data in the EU since 2018. For cookies, this means: without consent, only cookies that are strictly necessary for operating the website are allowed, for example for the shopping cart or security. All others – for web analytics or advertising, for example – require active consent (opt-in). Users must be informed clearly beforehand and give their consent deliberately; pre-ticked boxes are not sufficient.
On this basis, Germany's Federal Court of Justice (BGH) ruled in 2020 in the “Planet49” case that cookies for advertising and analytics may only be set with active consent. Since 1 December 2021, German law has explicitly required this (TTDSG, renamed TDDDG in May 2024).
Google Chrome and third-party cookies: what does the future hold?
For years, Google announced that it would phase out third-party cookies in Chrome and replace them with the “Privacy Sandbox” and interfaces such as the Topics API. In 2024 and 2025, Google backed away from this: third-party cookies remain in Chrome, and most Privacy Sandbox technologies have been discontinued. Safari and Firefox, on the other hand, have blocked third-party cookies by default for years. For online shops, this means: if you rely on third-party data, you lose a growing share of measurement data. First-party data and server-side tracking are more robust – something to consider right from the start of shop development.